See and control what AI agents do across model providers, MCP servers, repositories and endpoints.
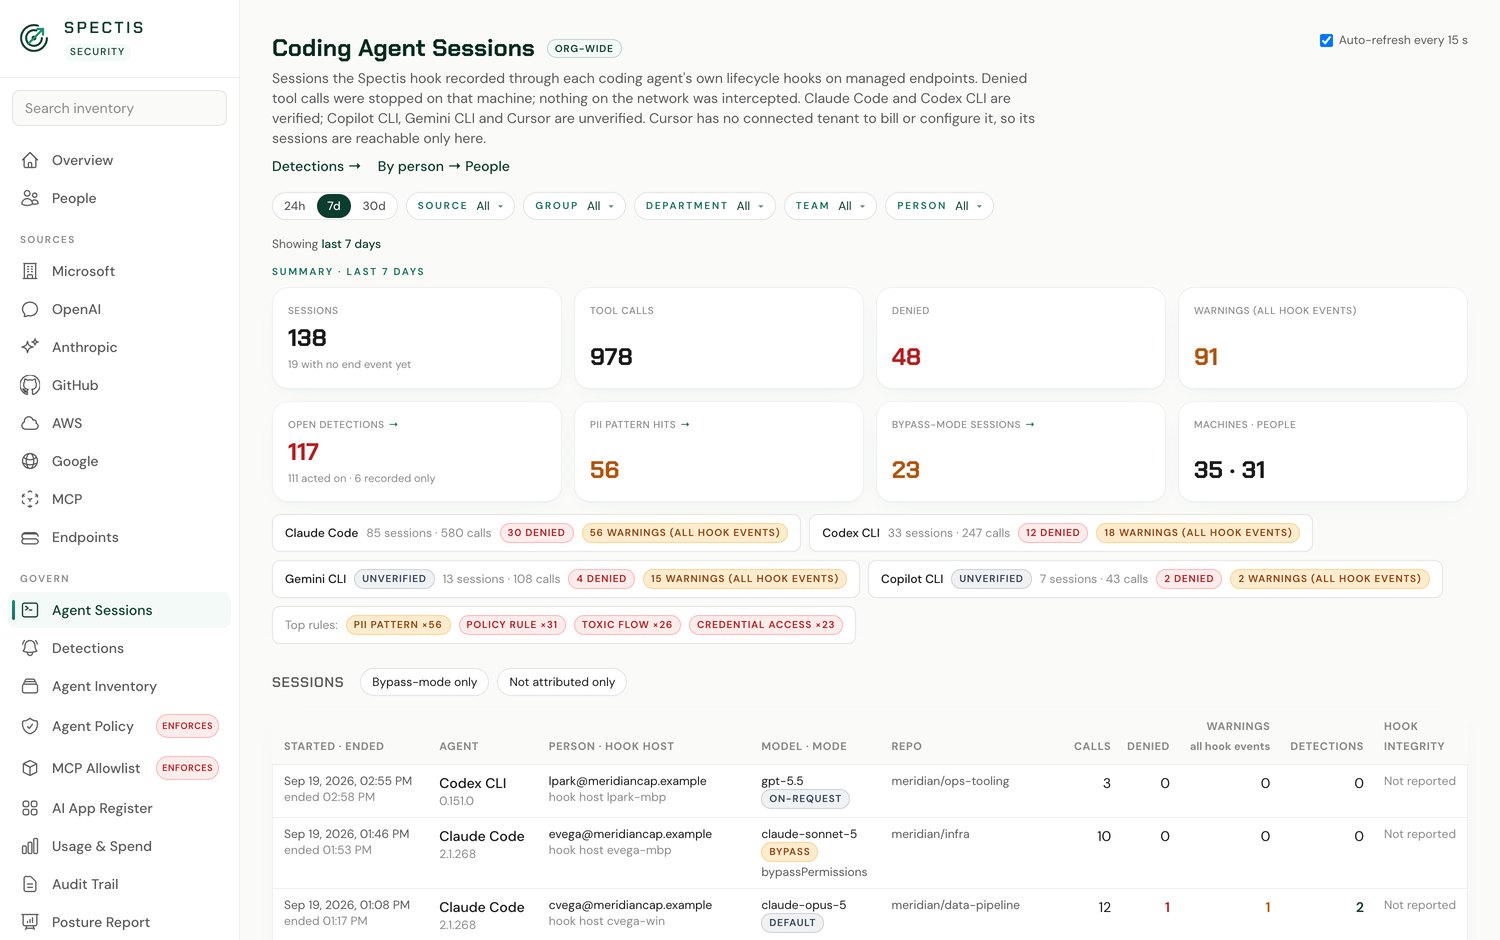
Coding agents read source code, run shell commands and call tools on your endpoints every day. Spectis records each action, attributes it to a named user, and blocks the actions your policy prohibits — with no proxy and nothing in your network path.
| 17:09:53 | Read | allow | src/app.py | 0.5 ms |
| 17:11:04 | Bash | allow | git commit -m 'wip' | 2.9 ms |
| 17:11:19 | Bash | deny | git push — blocked by policy shell.git-push | 3.4 ms |
| 17:11:42 | Bash | warn | cat customers.csv — customer data in tool output | 4.1 ms |
One request to an agent touches more systems than any single log records.
A developer asks a coding agent to fix a bug. It calls a model API, opens two MCP servers, reads a repository and runs commands on a laptop. Each step leaves a trace somewhere different, under a different identifier — when it leaves one at all. Spectis gathers those traces and ties them to the person who started it.
One record per person
Activity from every provider, server, repository and machine resolves to the individual who ran it — not to an API key, a hostname or a shared service account. That record is what you hand an auditor.
No proxy, no latency
Spectis reads each provider’s own administrative record rather than inspecting traffic. On the endpoint it runs an agent, as endpoint security does. Nothing sits between your people and the tools they use, and nothing competes with your existing network stack.
Two places it acts
Everywhere else Spectis only watches. It enforces in exactly two: the policy your coding agents apply before an action runs, and the allowlist of MCP servers they are permitted to reach.
A complete inventory of AI agents, activity and risk across your organisation.
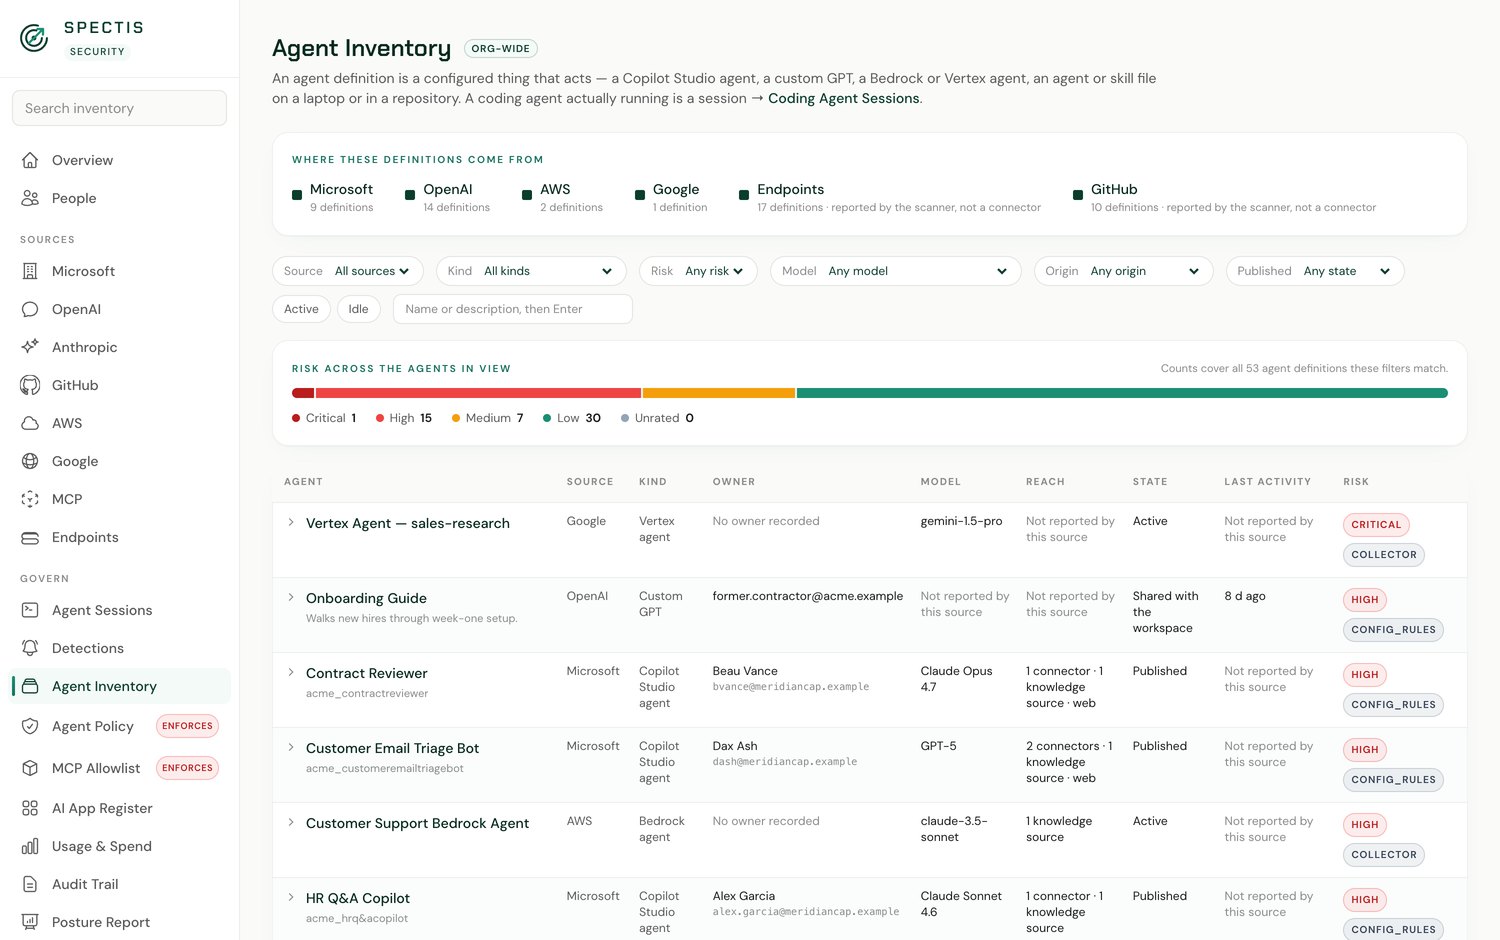
Agent inventory and ownership
Every configured agent across every connected source — Copilot Studio agents, custom GPTs, Bedrock and Vertex agents, and the agent and skill files held in repositories and on endpoints — with its owner, model and reach, including the agents that have no assigned owner.
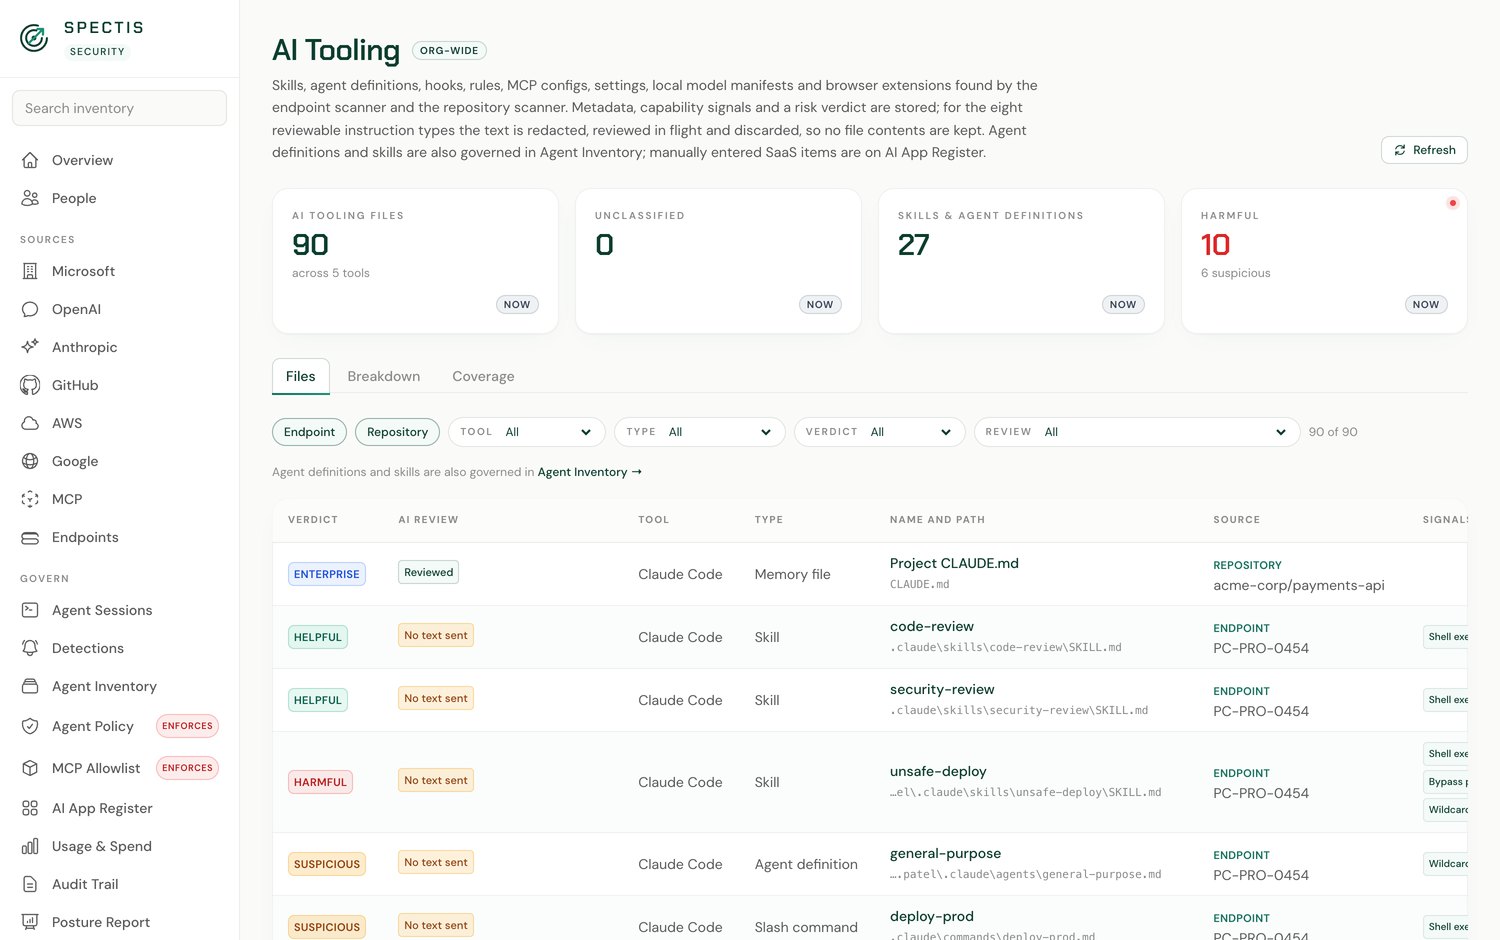
Risk analysis with stated reasoning
Spectis analyses the instruction files your agents load and reports which of them present a risk, with a written rationale a reviewer can act on rather than a rule identifier and a score.
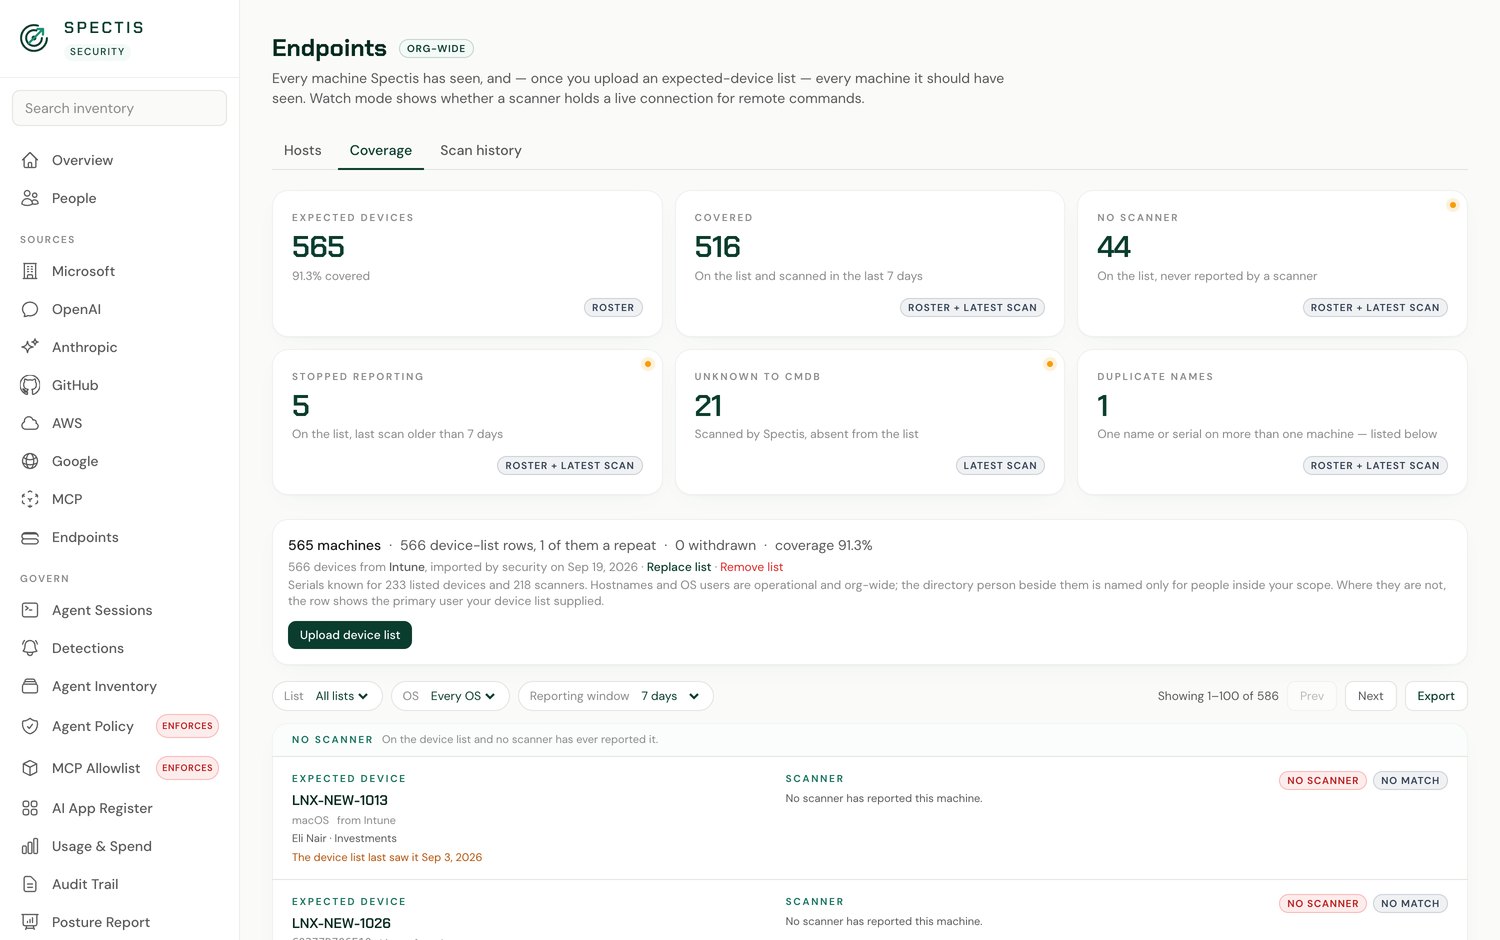
Verified endpoint coverage
Upload the device list you already maintain. Spectis reconciles it against the endpoints that have reported and categorises every gap: machines without a scanner, machines that have stopped reporting, and machines absent from your inventory.
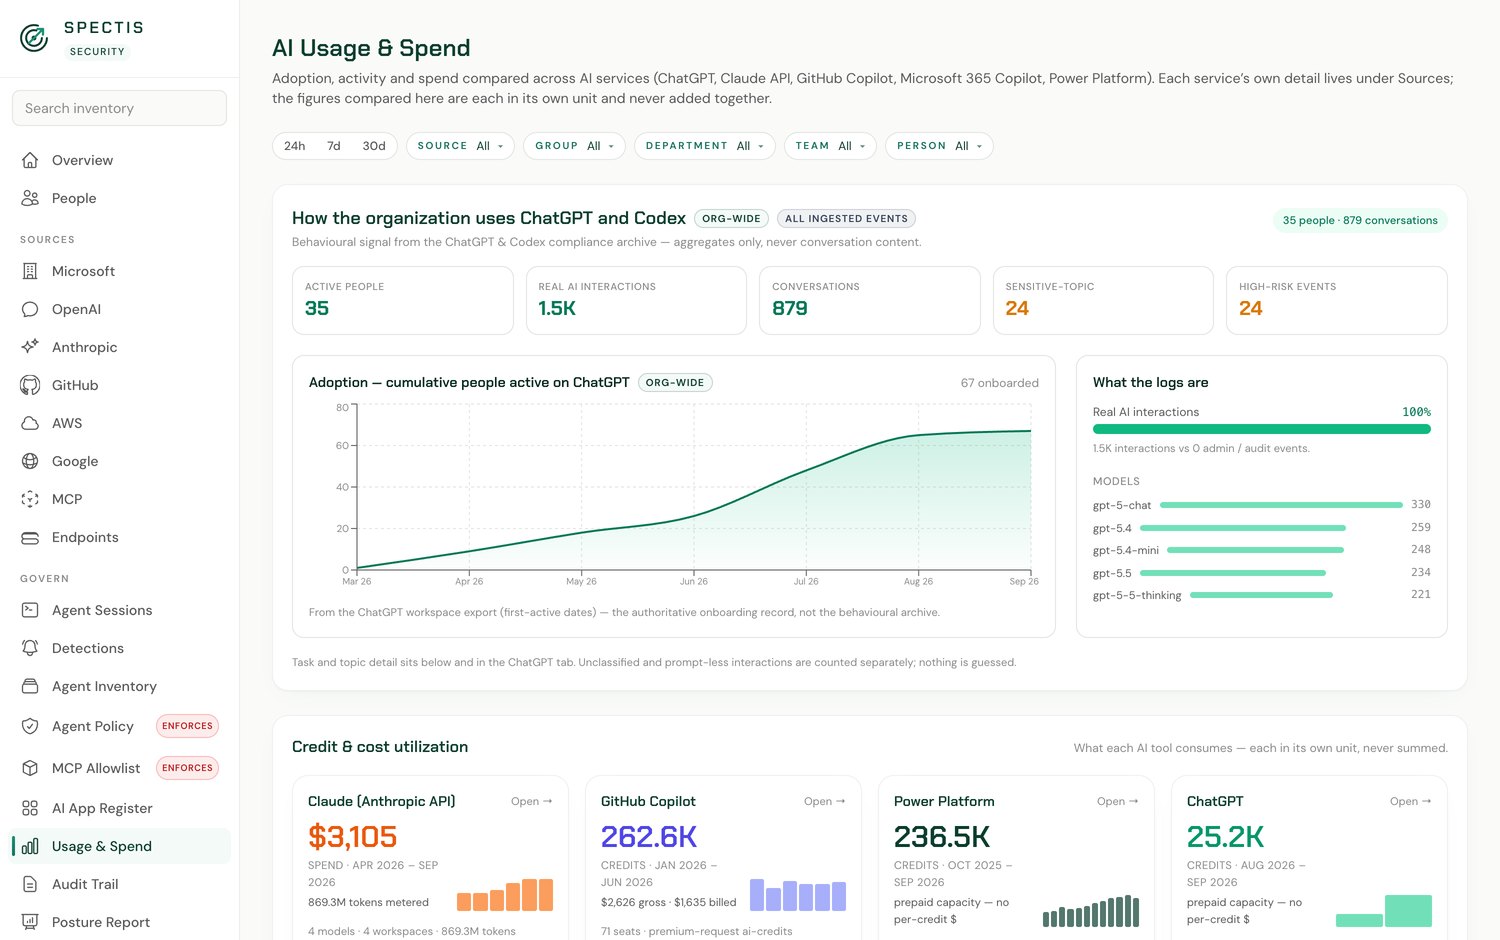
AI spend by team and provider
Adoption and cost reported per user, team and provider, each in that provider’s own unit and never blended into a single figure.
Connected sources
Screens show example data from a demonstration tenant.
Policy enforced at the agent, before the action executes.
Coding agents request permission before each tool call, and Spectis answers that request. Write a rule, scope it to a user, group or department, and publish it. The decision is then made on the endpoint itself, in milliseconds, whether or not it can reach us.
deny   git push
on     every coding agent
except group "Cyber Team"
Every rule is tested before publication and signed per user, so an endpoint only applies policy it can prove originated with you.
p95 added to each tool call, against a 10 ms budget.
network calls on the decision path. It works offline.
correlated to a single user and timeline.
AI clients discovered and inventoried on each endpoint.
Ask Spectis
Coming soonAsk in plain language: who is using which agent, which MCP servers turned up this week, what was flagged malicious and why. You get an answer with the evidence behind it, scoped to what your role is allowed to see.
Exposure graph
Coming soonOne view of the full path: user, endpoint, agent, the MCP servers it can reach, the models behind them and the data involved — so exposure that arises from a combination of individually acceptable conditions is visible in a single place.
What Spectis collects, and what it never does.
Out of the traffic path
No proxy, no interception, no certificate to install. An interruption to Spectis does not interrupt engineering work.
Prompts are not captured
Spectis records that an agent ran a command and the verdict it received, not what anyone typed. Conversation content is reachable by Compliance alone, and every read is audited.
Secrets never travel
Environment variable names, never values. No raw command lines. Credentials found during a scan are reported by type and masked, never carried in the clear.
Analysis retains nothing
Where an instruction file requires closer analysis it is examined and discarded. Spectis retains the verdict, not the file, and will run the analysis inside your own cloud account.
Administrators see no usage data
The people who operate the platform cannot read who used which AI service. That separation is built into the data model rather than configured as a setting.
Your SIEM remains the system of record
Audit events stream to Splunk, Sentinel, syslog or a webhook. Spectis is a source of evidence, not another console to staff.
Full data-handling documentation, the access-control contract and our security questionnaire responses are available for review during evaluation.
Deployed in a dedicated tenant, or entirely on your own infrastructure.
Managed single-tenant
A dedicated instance with its own orchestrator, dashboard and database. Encrypted at rest, TLS 1.3 in transit, with no shared data plane between customers.
Self-hosted
Docker Compose or Helm, in your cloud or on-premises. Identical to the hosted build, with no features reserved for the managed edition.
Identity-aware
SCIM provisioning with your directory groups mapped to roles.
Role-scoped by design
Five roles with a written access contract and an audit trail over every privileged read.
Signed control plane
Every instruction sent to an endpoint is signed and verified before it acts.
Start with a single engineering team.
Install the scanner on one team’s endpoints, connect the providers you already pay for, and we will review the results with you. Nothing is introduced into your traffic path, and nothing needs to be unpicked if you decide against it.